Every article about NAT explains it and then leaves you with nothing to type. So here’s the configuration first, the theory second.
What is NAT? Network Address Translation rewrites the IP addresses in a packet header as it crosses a router, so devices holding private addresses can reach the public internet through one or more public addresses. Three flavours exist: static NAT (one to one, fixed), dynamic NAT (a pool, first come first served), and PAT, also called NAT overload (many to one, separated by port number).
All three, on the same Cisco topology. Inside network is 192.168.1.0/24, the WAN link is 203.0.113.2.
Step one is identical for all three. Tell the router which side is which:
interface GigabitEthernet0/0
 ip address 192.168.1.1 255.255.255.0
 ip nat inside
!
interface GigabitEthernet0/1
 ip address 203.0.113.2 255.255.255.0
 ip nat outside
Static NAT. One line. Your web server at .10 is permanently reachable at 203.0.113.5:
ip nat inside source static 192.168.1.10 203.0.113.5Dynamic NAT. A pool of eleven public addresses, handed out as needed:
ip nat pool PUB-POOL 203.0.113.10 203.0.113.20 netmask 255.255.255.0
access-list 1 permit 192.168.1.0 0.0.0.255
ip nat inside source list 1 pool PUB-POOL
PAT (NAT overload). The whole subnet behind the WAN interface address:
access-list 1 permit 192.168.1.0 0.0.0.255
ip nat inside source list 1 interface GigabitEthernet0/1 overload
Verify any of them the same two ways:
show ip nat translations
show ip nat statistics
That’s the working answer. Now here’s what each line is actually doing, why the third one is the only one you’ll meet in the wild, and the five mistakes that break it.
Three different things are called NAT. This article is about the networking one. If you landed here looking for NAT type 1, 2 or 3 on a console, skip to that section. If you meant NAT in medicine, that’s nucleic acid testing for blood screening, and you want a different site entirely.
What Is NAT Actually Doing? Follow One Packet
Your laptop can’t talk to the internet. Not directly.
It holds 192.168.1.11, which lives inside one of the private IP address ranges reserved by RFC 1918. Those addresses aren’t routable on the public internet. No ISP will carry them. Drop that packet on the open internet and it dies at the first hop.
So the router lies on your behalf.
Watch one HTTPS request to a server at 198.51.100.50 make the round trip:
| Stage | Source | Destination |
|---|---|---|
| 1. Leaves your laptop | 192.168.1.11:52104 | 198.51.100.50:443 |
| 2. Router rewrites, sends out Gi0/1 | 203.0.113.2:52104 | 198.51.100.50:443 |
| 3. Server replies to what it saw | 198.51.100.50:443 | 203.0.113.2:52104 |
| 4. Router rewrites back, sends to you | 198.51.100.50:443 | 192.168.1.11:52104 |
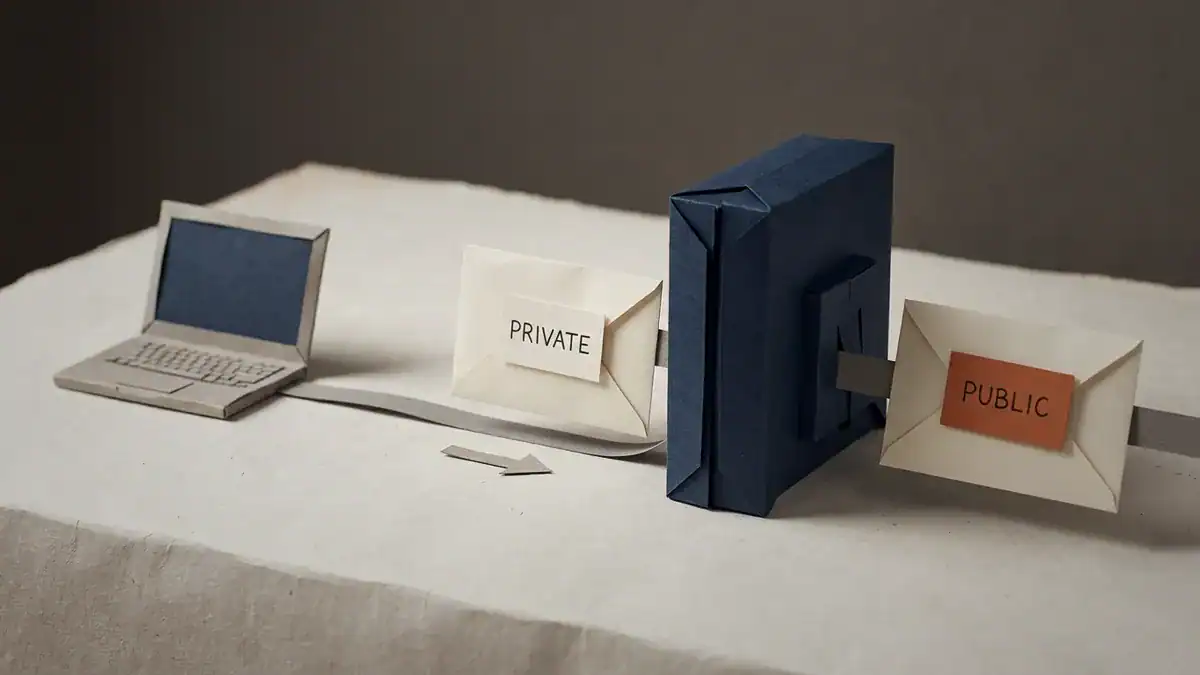
The envelope never changes. Only the address on the front of it does, and the router is where that happens.
Step 2 is the translation. Step 4 is the router remembering it did step 2.
That memory is the NAT table, and it’s the whole trick. When the router rewrites a source address, it writes a row recording what it swapped. The reply comes back addressed to the public address, the router looks up the row, and reverses the swap. No row, no reply gets home.
Which is why NAT is a stateful process, not a protocol. Nothing speaks NAT. There’s no NAT header, no NAT port, no NAT handshake. It’s a router function defined in RFC 2663 and RFC 3022, and the device on the far end has no idea it happened.
Grab the commands. Our free Cisco Commands Cheat Sheet PDF has the NAT block plus the other 200-odd IOS commands you’ll type on exam day. No email gymnastics.
Inside Local, Inside Global: the Four Terms That Trip Everyone Up
Cisco names the four addresses in a translation, and the names look backwards until they click.
| Term | What it means | In our example |
|---|---|---|
| Inside local | Your host’s real private address | 192.168.1.11 |
| Inside global | How your host looks to the outside world | 203.0.113.2 |
| Outside global | The remote host’s real public address | 198.51.100.50 |
| Outside local | How the remote host looks to your inside hosts | 198.51.100.50 |
Here’s the decoder. Inside and outside tell you whose network the host belongs to. Local and global tell you which side of the router you’re standing on when you look at it.
So “inside global” isn’t a contradiction. It’s your host (inside), seen from the public side (global).
Outside local and outside global usually match, because you’re not normally translating the far end’s address. They differ only in designs where you’re also rewriting destinations, which is rare outside of overlapping-subnet merges.
Now the real thing:
R1# show ip nat translations
Pro  Inside global      Inside local       Outside local       Outside global
tcp  203.0.113.2:52104  192.168.1.11:52104 198.51.100.50:443   198.51.100.50:443
tcp  203.0.113.2:52105  192.168.1.12:52104 198.51.100.50:443   198.51.100.50:443
tcp  203.0.113.2:1043   192.168.1.13:1043  198.51.100.80:80    198.51.100.80:80
Look at rows one and two. Two different laptops both picked source port 52104, which happens more often than you’d guess. The router kept 52104 for the first one and bumped the second to 52105. That’s PAT doing the only thing that makes many-to-one possible.
Ports are the entire reason one public address can carry a whole office.
Static NAT: One Private IP, One Public IP
Static NAT is a permanent, hand-written, one-to-one mapping. Address A always becomes address B, in both directions.
ip nat inside source static 192.168.1.10 203.0.113.5Two things make static NAT different from the other two.
It’s bidirectional. Dynamic NAT and PAT only build an entry when an inside host sends something out. Static NAT works from the outside in too. Someone on the internet hits 203.0.113.5, the router translates the destination to 192.168.1.10 and forwards it. That’s the point of it.
One server, one address, pinned down, and the arrow points both ways. That last part is what the other two can’t do.
The entry exists before any traffic does. Configure it and check straight away:
R1# show ip nat translations
Pro  Inside global   Inside local    Outside local   Outside global
---  203.0.113.5     192.168.1.10    ---             ---
Dashes in the outside columns mean the mapping is loaded and waiting. Dynamic entries never look like this. If you configured a static mapping and don’t see this row, the command didn’t take.
When you’d actually use it: publishing a server. A mail server, a VPN concentrator, a web server that needs a stable public address for DNS to point at. You need a spare public IP for each one, which is exactly why nobody uses static NAT for user traffic.
Want to publish only one port instead of the whole host? Static PAT, sometimes called port forwarding:
ip nat inside source static tcp 192.168.1.10 80 203.0.113.5 80That exposes port 80 and nothing else. Safer, and it lets several internal servers share one public address on different ports.
Dynamic NAT: A Pool, First Come First Served
Dynamic NAT hands out public addresses from a pool, one per inside host, and takes them back when the session ages out.
ip nat pool PUB-POOL 203.0.113.10 203.0.113.20 netmask 255.255.255.0
access-list 1 permit 192.168.1.0 0.0.0.255
ip nat inside source list 1 pool PUB-POOL
Three parts. The pool is the range of public addresses you own. The access list says which inside hosts are allowed to be translated. The ip nat inside source line marries them.
That access list is the part people get wrong, because 0.0.0.255 is a wildcard mask, not a subnet mask. Wildcards invert: a zero bit means “must match”, a one bit means “don’t care”. If wildcard masks still feel like a coin flip, our subnetting guide works through them with practice questions.
Now the failure mode, because dynamic NAT has a nasty one.
Eleven addresses in that pool. Bring a twelfth host online and it gets nothing. No error on the client, no log entry anybody checks, just a laptop that can’t load a page while the eleven around it work fine. And which laptop fails changes every time, because it depends on who asked first.
Three got an address. The fourth turned up late and the tray was bare. Nobody tells it why.
The tell is in the statistics:
R1# show ip nat statistics
Total active translations: 11 (0 static, 11 dynamic; 0 extended)
Hits: 84120  Misses: 2043
Misses climbing means the pool ran dry. Hits are packets that found a translation, misses are packets that needed a new one and couldn’t get it. Zero is the number you want.
Honestly? Dynamic NAT is close to a museum piece. It burns one public IPv4 address per concurrent host, and those cost real money now. It survives mostly on exams and in a few legacy designs. Learn it because Cisco tests it, then reach for the next one.
PAT (NAT Overload): One Public IP, Thousands of Sessions
This is the one that runs the internet.
access-list 1 permit 192.168.1.0 0.0.0.255
ip nat inside source list 1 interface GigabitEthernet0/1 overload
One word does all the work. overload tells the router to add the Layer 4 port number to each translation, which turns a one-to-one mapping into a one-to-many mapping. Your entire office goes out behind the single address sitting on Gi0/1.
Four conversations in, one cable out. The tags are the port numbers, and they’re the only reason the replies find their way home.
You can overload a pool too, if you have a handful of public addresses and a lot of users:
ip nat pool PUB-POOL 203.0.113.10 203.0.113.12 netmask 255.255.255.0
ip nat inside source list 1 pool PUB-POOL overload
Three addresses, tens of thousands of sessions. The router fills the first address’s port space before moving to the second.
A detail worth knowing, because it shows up in packet captures and confuses people: IOS tries to preserve your original source port. It only picks a new one on collision, and it stays inside the same range the original came from. Rows one and two of that translation table earlier are exactly this behaviour, 52104 kept and 52105 assigned.
Check PAT is running with the extended count:
R1# show ip nat statistics
Total active translations: 247 (0 static, 247 dynamic; 247 extended)
Outside interfaces:
  GigabitEthernet0/1
Inside interfaces:
  GigabitEthernet0/0
Hits: 918442  Misses: 0
Dynamic mappings:
-- Inside Source
[Id: 1] access-list 1 interface GigabitEthernet0/1 refcount 247
Extended means port-aware. If that number is zero while the dynamic count is high, overload didn’t make it into your config and you’re running plain dynamic NAT without knowing it.
Ready to build all three yourself? The SMEnode Labs CCNA Workbook ships the NAT lab as a runnable topology, not a screenshot. Boot it, break it, fix it.
Static vs Dynamic NAT vs PAT
| Static NAT | Dynamic NAT | PAT (overload) | |
|---|---|---|---|
| Mapping | 1 private to 1 public, permanent | 1 private to 1 public, temporary | Many private to 1 public |
| Public IPs needed | One per host | A pool | One, usually the WAN interface |
| Inbound connections | Yes, always | No, outbound must open the entry | No, needs static PAT |
| Entry appears | The moment you configure it | On first matching packet | On first matching packet |
| Entry disappears | Never, it’s in the config | Session timeout | Session timeout |
| Uses ports | No | No | Yes, that’s the point |
| Where you’ll meet it | Published servers | Exams, legacy designs | Every home and branch router |
| Command | ip nat inside source static | ...source list N pool NAME | ...source list N interface X overload |
If you remember one row, make it the last one. overload is the difference between NAT and PAT, and that’s the comparison Cisco keeps asking about.
How Do You Verify and Troubleshoot NAT?
Four commands cover almost everything.
show ip nat translations          ! the NAT table, one row per active translation
show ip nat translations verbose  ! adds timers and flags
show ip nat statistics            ! hits, misses, which interfaces, which mappings
clear ip nat translation *        ! wipe all dynamic entries
debug ip nat                      ! live translation log, careful on production
clear ip nat translation * is the one to respect. It drops every active dynamic session on the router. Fine in a lab, disruptive at 2pm on a Tuesday.
The five things that actually break NAT
1. You forgot ip nat inside or ip nat outside. By a distance the most common. The translation config is perfect, nothing translates, and show ip nat translations is empty. Run show ip nat statistics and read the interface lists. Blank means the router doesn’t know which way is out.
2. The access list doesn’t match. Usually a wildcard mask typed as a subnet mask. Symptom is misses climbing with no matching translations. Confirm with show access-lists and watch whether the match counter moves.
3. Your ACL is too broad. A permit-everything NAT list will happily translate traffic headed for your site-to-site VPN or an internal subnet across the WAN, and that traffic just stops working. Deny the internal destinations at the top of the list, before the permit.
4. The pool is exhausted. Covered above. Misses climb, some hosts work and some don’t, and the set changes hour to hour. Add overload or widen the pool.
5. Stale entries after a config change. NAT translations don’t re-read the config. Change a mapping while sessions are live and the old rows keep serving the old behaviour until they age out. Clear them.
The order of operations nobody mentions
This one matters and you won’t find it in a glossary.
Inside to outside: the router routes first, then translates. Your outbound ACLs and route lookups see the original private address.
Outside to inside: the router translates first, then routes. Inbound ACLs on the outside interface see the public address, not the private one.
Get this backwards and you’ll write an inbound ACL permitting 192.168.1.10 that never matches a thing, because at the moment that ACL runs, the packet is still addressed to 203.0.113.5.
What Is NAT Type on Your Console? A Different Thing Entirely
If you searched “what is NAT” after your console told you your NAT type was strict, you want this section and none of the rest.
| Console label | What it means | Cause |
|---|---|---|
| Type 1 / Open | Console holds a public address directly | Modem in bridge mode, or a DMZ host |
| Type 2 / Moderate | Behind a normal router that’s cooperating | Standard home setup with UPnP working |
| Type 3 / Strict | Behind a router that won’t open inbound paths | UPnP off, or you’re behind carrier-grade NAT |
Those labels are Sony’s and Microsoft’s marketing names for how permissive your router’s NAT is. The underlying thing has a proper taxonomy.
The old one, from RFC 3489, gave four types: full cone, address-restricted cone, port-restricted cone and symmetric. You’ll still see “4 types of NAT” quoted from it all over the internet. It’s been deprecated. RFC 4787 replaced the cone model because it was imprecise, splitting the behaviour into two independent questions: how the router allocates the mapping, and how it filters what’s allowed to use it.
So when someone says there are four types of NAT and someone else says three, they’re both right and they’re talking about different things. Three is the Cisco configuration taxonomy: static, dynamic, PAT. Four is the deprecated STUN behaviour taxonomy. Exams want the first one.
Strict NAT that no amount of port forwarding fixes usually means CGNAT, which is coming up next.
What Is NAT Outside a Cisco Router?
Same idea, five different vocabularies.
FortiGate. Fortinet splits it in two. Source NAT rides on the firewall policy, either using the outgoing interface address or an IP pool you define. Destination NAT lives in a separate VIP object that maps a public address, and optionally a port, to an internal server. There’s also central NAT mode, which pulls both into their own ordered tables away from the security policies. If firewalls are where you’re headed, start with what a FortiGate actually is, then add a FortiGate VM to EVE-NG and configure it for real.
Cisco ASA and FTD. Object NAT and twice NAT, with a rule table that’s evaluated top down. Worth knowing which platform you’re on, since the Cisco ASA reached end of life for several models and the replacements behave differently.
AWS. Two things that both do translation and get confused constantly. An internet gateway performs one-to-one NAT for instances that hold a public IPv4 address. A NAT gateway does source NAT for instances sitting in a private subnet, so they can reach out without being reachable. It’s PAT, sold by the hour.
Linux. iptables -t nat -A POSTROUTING -o eth0 -j MASQUERADE, or the nftables equivalent. MASQUERADE is PAT with the interface address, same as the Cisco overload line.
Your ISP: carrier-grade NAT. Look at your router’s WAN address. If it starts with anything from 100.64 to 100.127, you don’t have a public IP at all. That’s the shared address space from RFC 6598, reserved in 2012 specifically so ISPs could NAT their subscribers a second time. Your traffic gets translated twice, once by your router and once by theirs.
Practical consequence: port forwarding on your own router does nothing, because the inbound connection never reaches it. That’s the strict NAT type that won’t budge, and the fix is a static IP from your ISP or a tunnel service.
Firewall NAT is its own skill. The FortiGate NSE4 Workbook covers SNAT, VIPs and central NAT with lab topologies that boot.
Is NAT a Security Feature? The Honest Answer
Half credit.
NAT does block unsolicited inbound traffic, and that’s genuinely useful. Someone scanning your public address finds one device, and packets aimed at hosts behind it have nowhere to go, because no translation entry exists to tell the router where to send them.
But that’s a side effect of how translation works, not a security control. And it’s thin:
- It inspects nothing. Malicious traffic inside an allowed session sails through.
- It does nothing about outbound. Malware phoning home gets NAT’d out like any other traffic.
- Once a session is open, the return path is open with it.
- UPnP and NAT-PMP let any device on your LAN punch its own hole through, and plenty of consumer gear ships with that switched on.
- Static NAT and static PAT deliberately undo the protection, which is the whole reason you configured them.
Treat NAT as address arithmetic that happens to reduce your attack surface. Put a stateful firewall in front of anything you care about, with rules you wrote on purpose.
Does NAT Go Away With IPv6?
Not soon. And the numbers are the interesting part.
Native IPv6 crossed 50% of Google’s users on 2026-03-28, the first time the majority of traffic to one of the internet’s largest properties arrived over IPv6 (Google IPv6 statistics). Eighteen years after Google started counting. A genuine milestone.
NAT didn’t move.
Three reasons it’s staying. Almost everything runs dual stack, so the IPv4 half still needs translating. ISPs that have deployed IPv6 are still running CGNAT on the IPv4 side for the same customers. And enterprise networks with IPv4 baked into ACLs, licences and monitoring aren’t renumbering for fun.
IPv6 does have NAT66 and NPTv6. Both exist, both are discouraged, and the IETF’s position is that IPv6 has enough addresses that translating them is a design smell rather than a necessity.
So you’ll keep configuring NAT. Plan on it for your whole career.
NAT on the CCNA Blueprint
NAT isn’t optional on the exam, and it’s a configure-and-verify topic, not a recall one.
On the current CCNA 200-301 v1.1 blueprint it’s topic 4.1 in the IP Services domain, worth 10% of the exam: “Configure and verify inside source NAT using static and pools.” Read that wording carefully. Configure and verify. You’re expected to type the commands and read the output, which is exactly what this article walked through.
Cisco published the v2.0 blueprint on 2026-05-20, the first restructure since 2019. First date to test v2.0 is 2027-02-03, and the last date for v1.1 is 2027-02-02. IP Services didn’t survive as its own domain, the content folded into the new section 5.0 alongside the AI and network operations material. Our breakdown of what changed in the CCNA v2.0 blueprint has the full domain map.
Either blueprint, NAT is on it. Sitting the exam before February 2027? Study it as topic 4.1. After? Same commands, new section number.
CompTIA covers it more lightly. Network+ N10-009 wants the concepts and the NAT-versus-PAT distinction, not the Cisco syntax. If you’re choosing between the two, CCNA or Network+ breaks down which one fits where you are. And the free CCNA 200-301 practice test PDF will tell you fast whether your NAT is exam-ready.
Build the NAT Lab Yourself
Reading NAT config teaches you the syntax. Breaking NAT config teaches you NAT.
Minimum viable topology, four nodes:
- R1, your NAT router. Gi0/0 to the inside switch at 192.168.1.1/24, Gi0/1 to the outside at 203.0.113.2/24
- A switch, with two or three PCs on 192.168.1.0/24
- R2, playing the internet. 203.0.113.1/24 on the link, plus a loopback at 198.51.100.50 to act as a server
- A default route on R1 pointing at 203.0.113.1
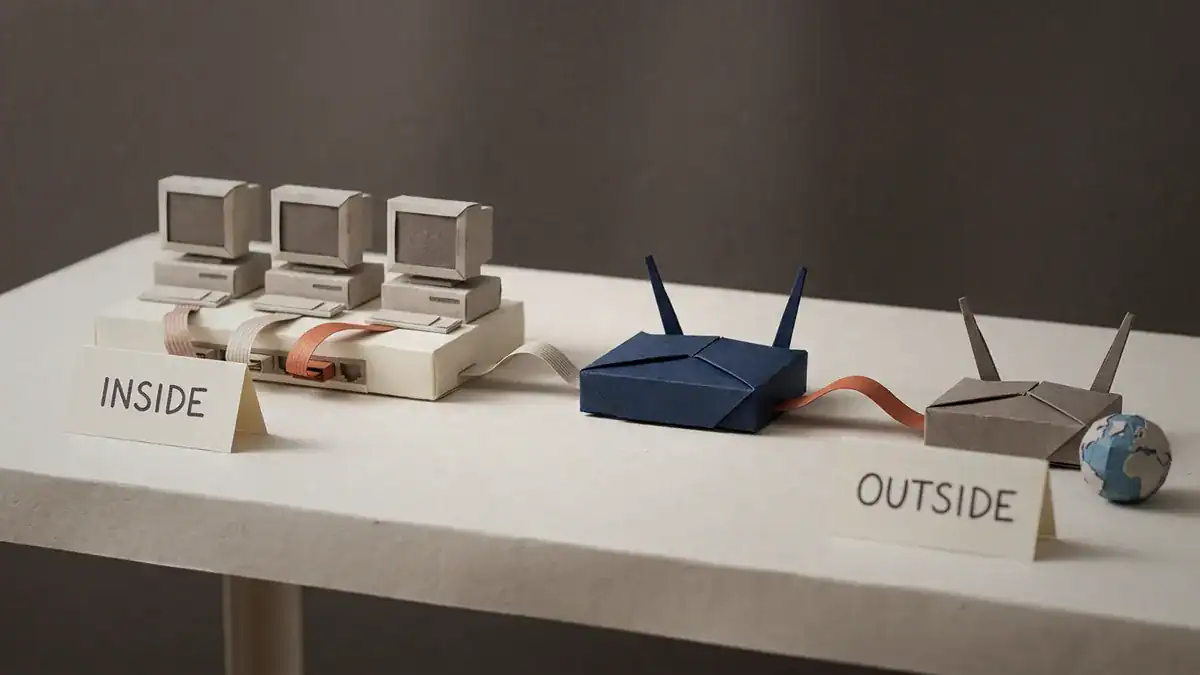
Four nodes and one orange cable. Everything in this article happens at the navy box in the middle.
Five things to do with it, in order:
- Configure PAT. Ping from two PCs at once and watch
show ip nat translationsfill up - Remove
ip nat insidefrom Gi0/0. Watch everything die. That’s failure mode one, and you should recognise it on sight - Swap to dynamic NAT with a two-address pool, then bring a third PC up and find the misses
- Add a static mapping for a PC and ping it from R2. Only static NAT lets you do that
- Type the wildcard mask backwards on purpose and work out what the symptom looks like
Build it in Packet Tracer or EVE-NG. Packet Tracer handles this topology fine and costs nothing. EVE-NG runs the real IOS image, which matters once you’re adding VLANs and routing protocols on top.
Not set up yet? Our guide to building a home lab for network engineers gets you running in a weekend, and there’s a list of CCNA labs you can build free in EVE-NG plus the topologies worth building before exam day.
Frequently Asked Questions
What is NAT in simple terms? It’s your router swapping your device’s private address for its own public one on the way out, then swapping it back on the way in. One public address, a whole household behind it.
Is NAT a protocol? No. Nothing speaks NAT, there’s no NAT header and no handshake. It’s a router function described in RFC 2663 and RFC 3022. The far end never knows it happened.
What are the 4 types of NAT? Depends who’s asking. Cisco teaches three: static, dynamic and PAT. The “four types” you’ll see quoted come from RFC 3489’s cone taxonomy, which RFC 4787 deprecated years ago. Exams want the three.
What’s the difference between NAT and PAT? PAT is NAT plus port numbers. Plain NAT maps one private address to one public address. PAT adds the Layer 4 port to each entry, so many private addresses can share one public address. On Cisco IOS it’s the overload keyword.
What is a NAT IP address? Loose phrasing for either side of a translation. Cisco’s precise terms are inside local (your real private address) and inside global (how you appear publicly).
What’s the difference between NAT and DHCP? Different jobs. DHCP hands your device an address when it joins the network. NAT rewrites that address when your traffic leaves. Your home router runs both, which is why they get confused.
Does NAT slow down my connection? Not measurably on modern hardware, since translation runs in the fast path. What it does break is anything wanting a direct inbound connection: peer-to-peer, some VoIP, some gaming, and hosting anything from home.
Is NAT the same as a firewall? No. It blocks unsolicited inbound traffic as a side effect, but it inspects nothing, stops no outbound traffic, and any device on your LAN can punch through it with UPnP.
Why does my router show 100.64.x.x on its WAN interface? You’re behind carrier-grade NAT. That’s RFC 6598 shared address space, and it means your ISP is translating you a second time. Port forwarding on your own router won’t work, because inbound connections never get that far.
Bottom Line
NAT rewrites addresses at the border and remembers what it rewrote. That’s it.
The five things worth carrying out of here:
- Static NAT is a permanent one-to-one map, works in both directions, and exists for servers you publish
- Dynamic NAT hands out a pool and runs dry, which is why you’ll mostly meet it on exams
- PAT adds port numbers so one public address carries thousands of sessions, and it’s what’s running on every router you own
show ip nat translationsandshow ip nat statisticsanswer nearly every NAT question you’ll be asked- Forgetting
ip nat insideorip nat outsideis the bug, more often than anything else on the list
Now go break it in a lab. Configure PAT, pull the ip nat inside line, and watch what the symptom looks like when you already know the cause. That’s the thirty seconds that saves you an hour on a live network some Tuesday.
Ready to go deeper? The SMEnode Labs CCNA Workbook ships NAT as a lab you boot, not a diagram you squint at, alongside the rest of the 200-301 topics.
Sources: Cisco, Configure Network Address Translation · Cisco Learning Network, CCNA exam topics · RFC 6598, IANA-Reserved IPv4 Prefix for Shared Address Space · Google IPv6 adoption statistics, figure as at 2026-03-28. Last reviewed 2026-09-20.