
Linux file permissions decide who can read, write or execute a file. Every file has three sets of rwx bits, one for the owner, one for the group and one for everyone else, and you change them with chmod, change who owns the file with chown, and set the defaults for new files with umask.
This page explains the logic behind each one: how to read rwx in ls -l, how symbolic and octal notation map to each other, and the mistake that wrecks a whole directory when you run chmod -R without thinking first. Grab the free PDF for the quick-reference version.
How Linux File Permissions Work: Who, What and How
chmod 755 isn’t hard to copy and paste. Understanding why it’s 755 and not 750 is where people get stuck.
Three separate ideas get bundled into one command: who can act on a file (owner, group, everyone else), what they can do (read, write, execute), and how you write that down (letters or a number). Miss one piece and you either lock yourself out of your own script, or leave a config file world-writable without noticing.
Reading Linux File Permissions with ls -l
Run ls -l on any file and you get a line like this:
-rwxr-xr-x 1 root staff 8192 Sep 16 10:02 deploy.shBreak down that 10-character block:
| Position | Meaning |
|---|---|
| 1st character | File type: - file, d directory, l symbolic link |
| Characters 2-4 | Owner’s permissions (rwx) |
| Characters 5-7 | Group’s permissions (rwx) |
| Characters 8-10 | Everyone else’s permissions (rwx) |
So -rwxr-xr-x reads as: a regular file, the owner can read, write and execute, the group and everyone else can read and execute. No write access outside the owner. That’s a normal, safe set for a script other people need to run but shouldn’t edit.
chmod Command: Symbolic vs Octal Notation
There are two ways to give chmod the same instruction. Pick whichever fits the job.
Symbolic notation changes permissions relative to what’s already there:
chmod u+x script.sh    # add execute for the owner
chmod g-w file.txt     # remove write from the group
chmod o=r config.yml   # set "others" to read-only, nothing more
chmod a+x setup.sh     # add execute for everyone
u (user/owner), g (group), o (other), a (all). + adds, - removes, = sets exactly, wiping whatever was there.
Octal notation sets the whole permission set at once, with three digits (owner, group, other). Each digit is a sum:
| Value | Permission |
|---|---|
| 4 | Read |
| 2 | Write |
| 1 | Execute |
Read + write + execute = 4+2+1 = 7. Read + execute = 4+1 = 5. Read only = 4.
| Octal digit | Symbolic |
|---|---|
| 0 | --- |
| 1 | --x |
| 2 | -w- |
| 3 | -wx |
| 4 | r-- |
| 5 | r-x |
| 6 | rw- |
| 7 | rwx |
Look up each digit, read left to right, and you’ve decoded any octal permission without a calculator. The full flag list lives in the chmod manual page.
chmod 755 vs 644 vs 777: The Numbers You’ll Actually Use
Three numbers cover most real work.
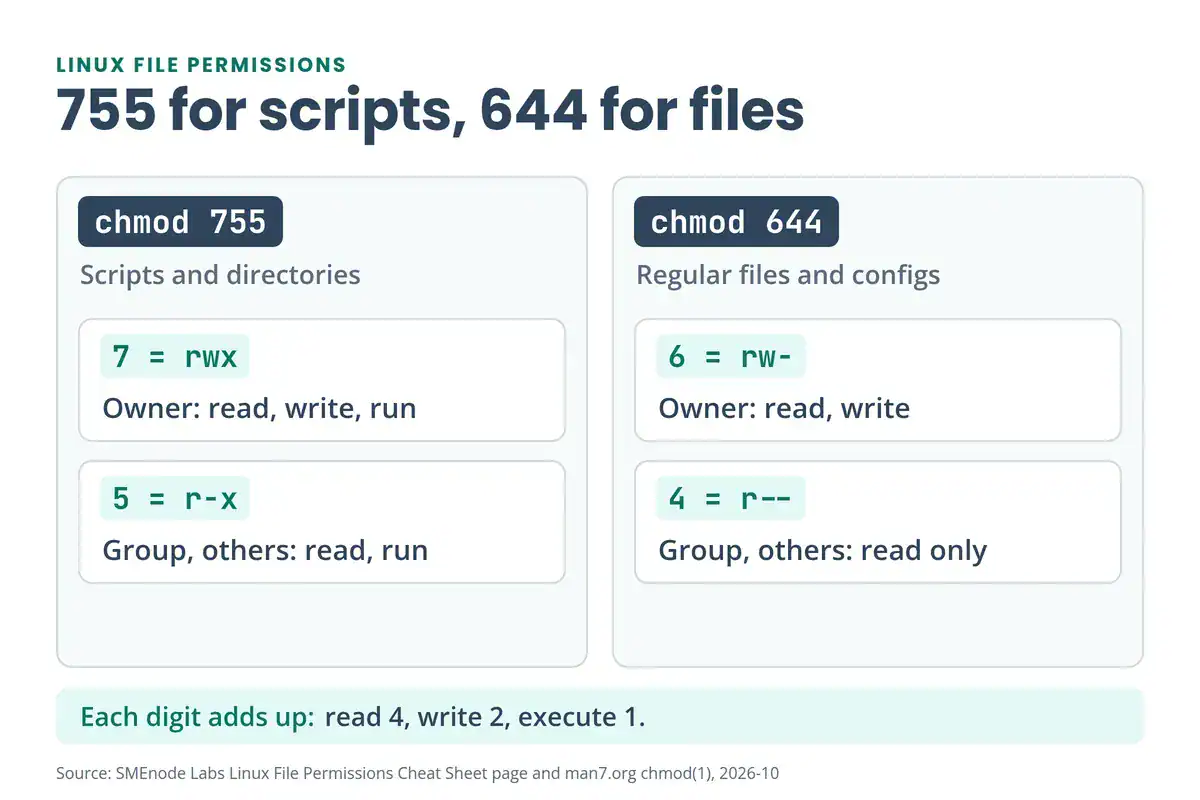
chmod 755 script.sh   # owner rwx, group r-x, other r-x
chmod 644 file.txt    # owner rw-, group r--, other r--
chmod 700 secret.key  # owner rwx, group and other: nothing
755 is for scripts and directories: everyone can run or enter it, only the owner can change it. 644 is for ordinary files and configs: everyone can read, only the owner can edit. 777 gives every user on the system full read, write and execute access. It’s almost never the right answer outside a throwaway test box. If you’re reaching for it to make an error go away, the real problem is usually ownership or the wrong user, and chown is the fix.
chmod Recursive: Changing Permissions on a Whole Directory
chmod -R applies a change to a directory and everything inside it. Sounds simple. It’s the most common way people break a deployment.
chmod -R 755 /var/www/appThis sets 755 on every file and every directory underneath, including files that had no business being executable. A directory needs the execute bit so you can enter it. A text config file doesn’t need execute at all. Blanket -R 755 marks every file in the tree executable, which is sloppy and hides real permission problems the next time something breaks.
The safer pattern separates files from directories:
find /var/www/app -type d -exec chmod 755 {} \;
find /var/www/app -type f -exec chmod 644 {} \;
Directories get 755, files get 644. If some files genuinely need to run, chmod +x them one by one afterwards.
There’s also a one-line version using capital X, which adds execute only to directories and to files that already have execute set for someone:
chmod -R u+rwX,go+rX,go-w /var/www/appThat’s the version worth remembering if you only take one thing from this section.
chown Command and chgrp: Changing Ownership
chmod controls what’s allowed. chown and chgrp control who it applies to.
chown deploy:www-data app.conf   # set owner to "deploy", group to "www-data"
chown deploy app.conf            # change owner only
chown :www-data app.conf         # change group only
chgrp www-data app.conf          # same as the line above, older syntax
chown -R deploy:www-data /srv/app  # apply to a whole directory tree
Ownership and permissions work together. chmod 640 on a file means nothing useful if the wrong user owns it. Check both when something “isn’t working” and the permission bits look correct.
If you automate servers, the Ansible file module sets owner, group and mode in one task. Our Ansible commands cheat sheet covers it.
Special Permissions: setuid, setgid and the Sticky Bit
Past read, write and execute, three special bits show up often enough to know on sight.
| Bit | Octal | What it does |
|---|---|---|
| setuid | 4000 | A program runs with the file owner’s privileges, not the user running it. passwd uses this so regular users can update a file only root can normally write. |
| setgid | 2000 | On a directory, new files inherit the directory’s group instead of the creator’s default group. Common on shared team folders. |
| sticky bit | 1000 | On a directory, only the file’s owner (or root) can delete or rename it, even if others have write access. /tmp uses this so one user can’t delete another user’s temp files. |
You’ll see these as a fourth leading digit: chmod 4755 sets setuid plus the usual 755. In ls -l they show up as s, S or t in place of the normal execute character.
umask and Default File Permissions in Linux
Ever notice a new file lands at 644 and a new directory at 755 without anyone running chmod? That’s umask.
Linux starts from a base of 666 for files and 777 for directories (new files never get execute by default). The umask removes bits from that base:
umask       # show the current value
umask 022   # set it
With the common default of 022, new files get 644 and new directories get 755. Change it to 002 on a shared project folder and new files come out group-writable, so the team doesn’t have to chmod after every save.
One catch: umask is a bit mask, not real subtraction. The kernel calculates 0666 & ~022, as the umask manual page shows. “666 minus 022” happens to give the right answer, but it breaks with odd digits. A umask of 033 gives files 644, not 633, because there was no execute bit to remove in the first place.
What’s Inside the Linux File Permissions Cheat Sheet PDF
- A permissions and ownership section covering
chmod(withchmod 755),chown user:group,chgrpandumask, one line each - The commands around it: 62 Linux commands across 8 groups, from file operations and text processing to processes, networking, disk, archiving and user management
- Format: 5 pages, printable
The deeper material, the octal table, the chmod -R pattern, special bits and the umask math, is on this page, so read the page and keep the PDF beside your keyboard.
Who It’s For
- CompTIA Linux+ and A+ candidates working through the Linux permission and ownership commands
- DevOps engineers who want to stop guessing at chmod numbers mid-deploy
- Junior sysadmins troubleshooting “permission denied” errors for the first time
- Anyone who’s run
chmod -R 777out of frustration and knows that’s not a real fix
Intermediate level. You should already be comfortable in a terminal before this one. If you’re still building that foundation, start with our Linux Commands Cheat Sheet PDF, which covers the 58 commands you’ll type before permissions come up.
No questions yet. Ask the first one.